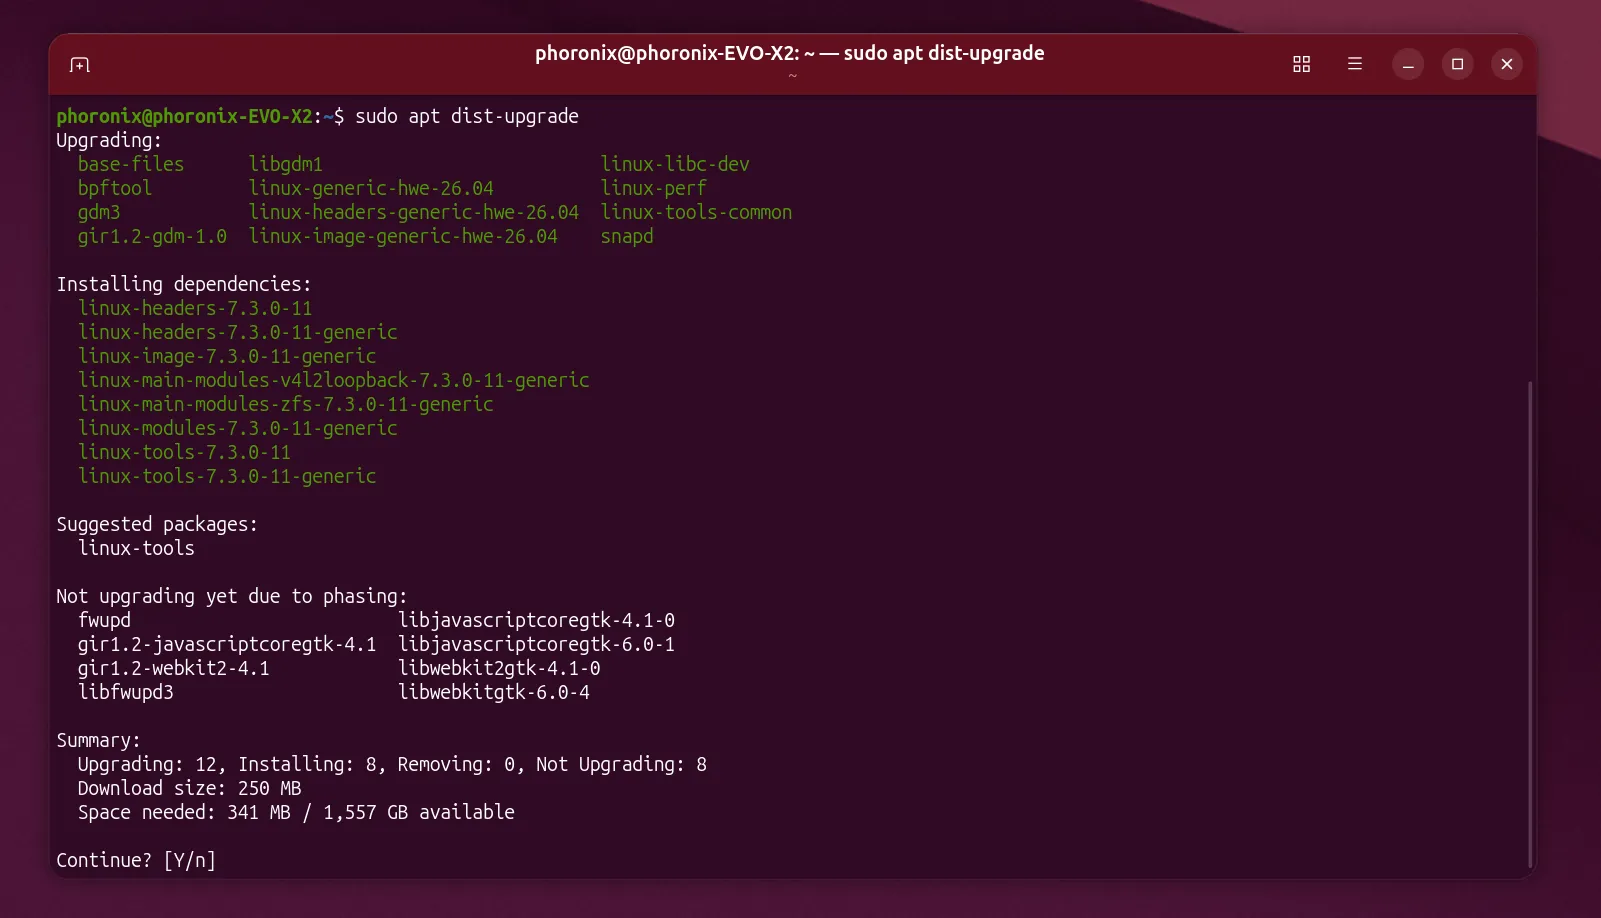
# Debian's APT Removing Some Features Due To Advancements In AI Security Discoveries Written by Michael Larabel in Debian on 19 November 2026 at 09:15 AM EST. ... Stemming from the recent Debian APT man-in-the-middle attack from a vulnerability in APT's downloading code and ongoing advancements in AI/LLMs around security research, APT is now resorting to disabling and removing some older, complex features that may make the program more vulnerable to finding exploits moving forward. Debian developer Julian Andres Klode announced that next week he will be removing support for various features in APT that are now declared end-of-life. The features planned for the near-immediate removal include support for repositories with detached Release.gpg signatures, repositories with only weak hashes like MD5 or SHA1, and repositories without hashes / Release file. Also being considered for removal are insecure repositories with the "allow-insecure" or "allow-downgrade-to-insecure" options, fallbacks to a different file if one route fails, and other non-essential features. Some features could be restored later if they are deemed "safe": "As we gain a better understanding of the control flow we m
- Key components named in the report: Debian.
- This is a release or availability story, so upgrade timing and rollback matter.
What happened
“Michael Larabel is the principal author of Phoronix.com and founded the site in 2004 with a focus on enriching the Linux hardware experience. Michael has written more than 20,000 articles covering the state of Linux hardware support, Linux performance, graphics drivers, and other topics. Michael is also the lead developer of the Phoronix Test Suite, Phoromatic, and OpenBenchmarking.org automated benchmarking software”
Phoronix Premium allows ad-free access to the site, multi-page articles on a single page, and other features while supporting this site's continued operations.
The mission at Phoronix since 2004 has centered around enriching the Linux hardware experience. In addition to supporting our site through advertisements, you can help by subscribing to Phoronix Premium. You can also contribute to Phoronix through tips/donations via PayPal or Stripe.
Why it matters
Linux runs a large share of the internet's servers, business infrastructure, and personal computers. A flaw that can be exploited in the kernel, OpenSSH, or another core component reaches far beyond one distribution, so the practical question is whether your systems are exposed and how quickly a tested fix is available.
What to do
- Check the official advisory for the affected versions and fixed versions.
- Apply the vendor update after a normal backup and a short test where possible.
- If a patch is not available yet, use the mitigations in the advisory and reduce exposure.
Read the original
The full report, including versions, affected systems and any vendor statement, is at Phoronix. Kituwa summarizes the headline and adds practical context for people running Linux servers, desktops and small-business systems.