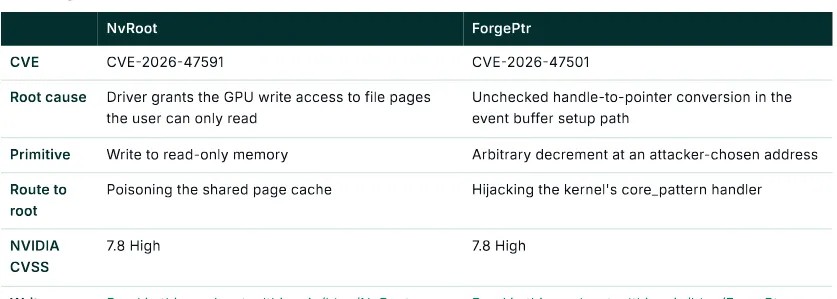
# NVIDIA NvRoot & ForgePtr Vulnerabilities Published For Linux Driver, 25 More Coming Written by Michael Larabel in NVIDIA on 12 November 2026 at 09:17 AM EST. ... In addition to Jensen Huang resigning, coincidentally the embargo just expired on the first two of 25 more NVIDIA graphics driver security vulnerabilities coming. ForgePtr and NvRoot are particularly volatile for those renting GPU slices in the cloud. Stealthium made public today ForgePtr (CVE-2026-47501) and NvRoot (CVE-2026-47591). With ForgePtr, an unprivileged process in a GPU container can go root on the host. With NvRoot, the GPU can rewrite files the OS has marked as read-only from any tenant on the node. These vulnerabilities have existed in the NVIDIA open kernel modules for the past four years and rated as CVE 7.8 "high" vulnerabilities. NvRoot is fixed by the NVIDIA 610.57.04 / 595.91.07 / 580.178.04 drivers while ForgePtr is fixed in 615.71.09. In a message to Phoronix, Stealthium says they have 25 more security disclosures to come that affect the NVIDIA AI runtime stack. Blog posts provide more details on NvRoot and ForgePtr.
- Tracked as CVE-2026-47501, CVE-2026-47591.
- Key components named in the report: NVIDIA.
What happened
“Michael Larabel is the principal author of Phoronix.com and founded the site in 2004 with a focus on enriching the Linux hardware experience. Michael has written more than 20,000 articles covering the state of Linux hardware support, Linux performance, graphics drivers, and other topics. Michael is also the lead developer of the Phoronix Test Suite, Phoromatic, and OpenBenchmarking.org automated benchmarking software”
Phoronix Premium allows ad-free access to the site, multi-page articles on a single page, and other features while supporting this site's continued operations.
The mission at Phoronix since 2004 has centered around enriching the Linux hardware experience. In addition to supporting our site through advertisements, you can help by subscribing to Phoronix Premium. You can also contribute to Phoronix through tips/donations via PayPal or Stripe.
Why it matters
Linux runs a large share of the internet's servers, business infrastructure, and personal computers. A flaw that can be exploited in the kernel, OpenSSH, or another core component reaches far beyond one distribution, so the practical question is whether your systems are exposed and how quickly a tested fix is available.
What to do
- Check the official advisory for the affected versions and fixed versions.
- Apply the vendor update after a normal backup and a short test where possible.
- If a patch is not available yet, use the mitigations in the advisory and reduce exposure.
Read the original
The full report, including versions, affected systems and any vendor statement, is at Phoronix. Kituwa summarizes the headline and adds practical context for people running Linux servers, desktops and small-business systems.