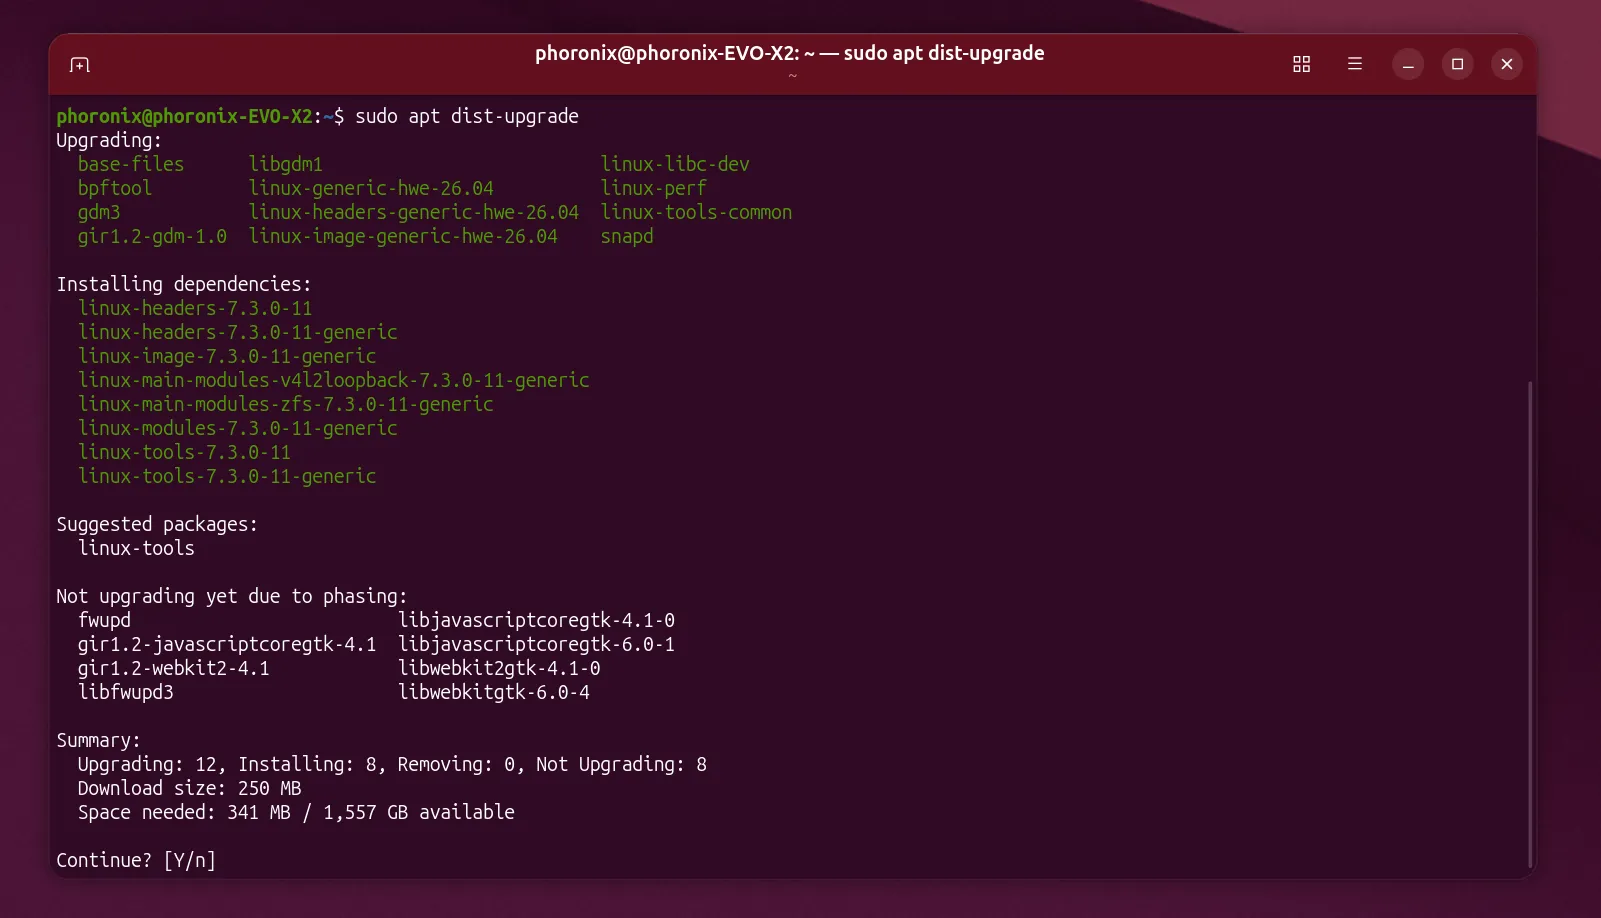
Canonical is giving Ubuntu Pro users early access to AI-generated patches for known security flaws, available through a new opt-in archive called Edge. To
- Key components named in the report: Ubuntu.
What happened
“Canonical is giving Ubuntu Pro users early access to AI-generated patches for known security flaws, available through a new opt-in archive called Edge.”
To get fixes out faster to customers and users, the company has built a multi-agent system called Surge to backport fixes for vulnerabilities in software packages.
The machine-generated patches land in the Edge archive. This is opt-in and not enabled by default. Ubuntu Pro Users who want fixes before they receive full testing or ‘qualification’, will need to manually enable the Edge archive on supported systems.
Why it matters
Linux runs a large share of the internet's servers, business infrastructure, and personal computers. A flaw that can be exploited in the kernel, OpenSSH, or another core component reaches far beyond one distribution, so the practical question is whether your systems are exposed and how quickly a tested fix is available.
What to do
- Check the official advisory for the affected versions and fixed versions.
- Apply the vendor update after a normal backup and a short test where possible.
- If a patch is not available yet, use the mitigations in the advisory and reduce exposure.
Read the original
The full report, including versions, affected systems and any vendor statement, is at OMG! Ubuntu. Kituwa summarizes the headline and adds practical context for people running Linux servers, desktops and small-business systems.